Port scan
Identify the exposed network surface on the authorized host.
Authorized operators only
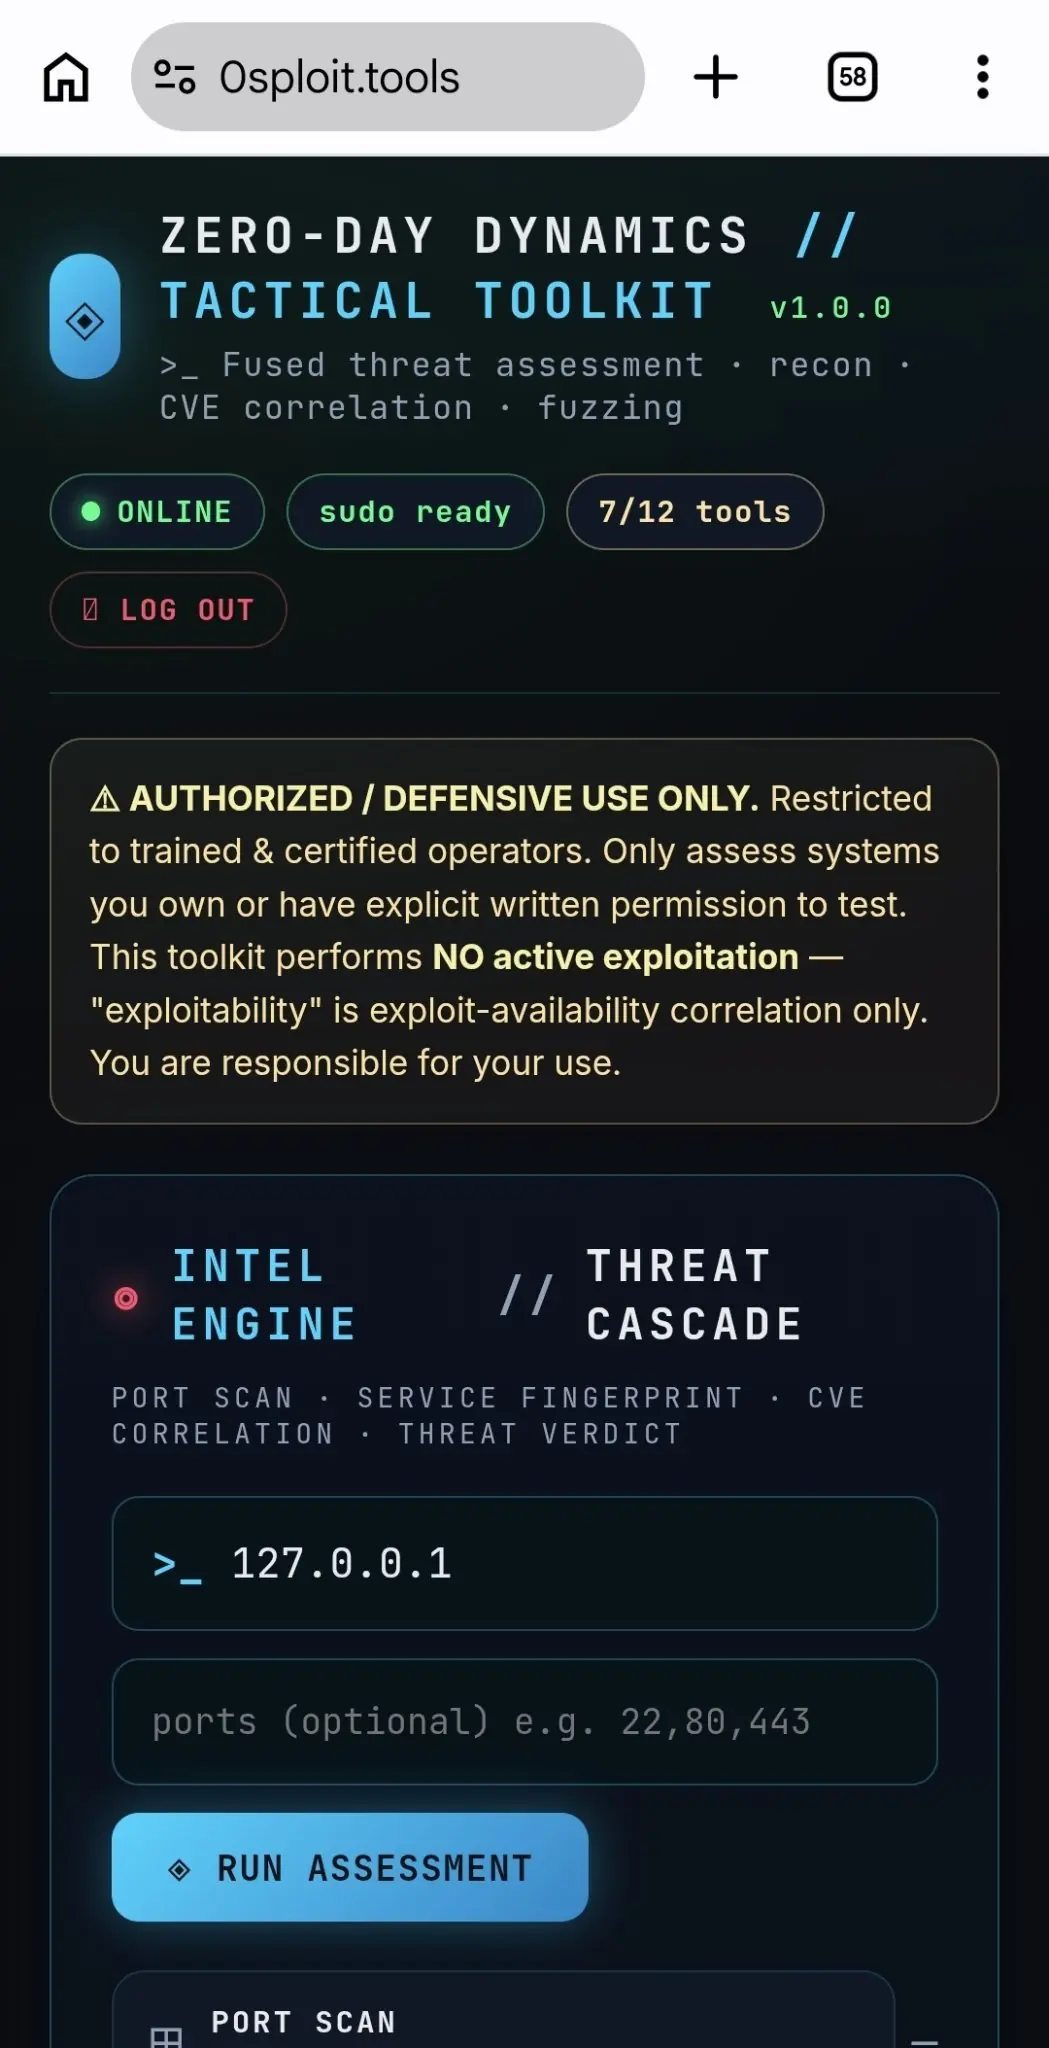
The active red-team half of the Zero-Day Dynamics stack. Where ZDD FIELD senses, 0sploit tests — turning network exposure into a clear sequence: discover, fingerprint, correlate, and actively validate integrity against live targets.
BOUNDARY: Use only on systems you own or have explicit written permission to assess.
Threat cascade
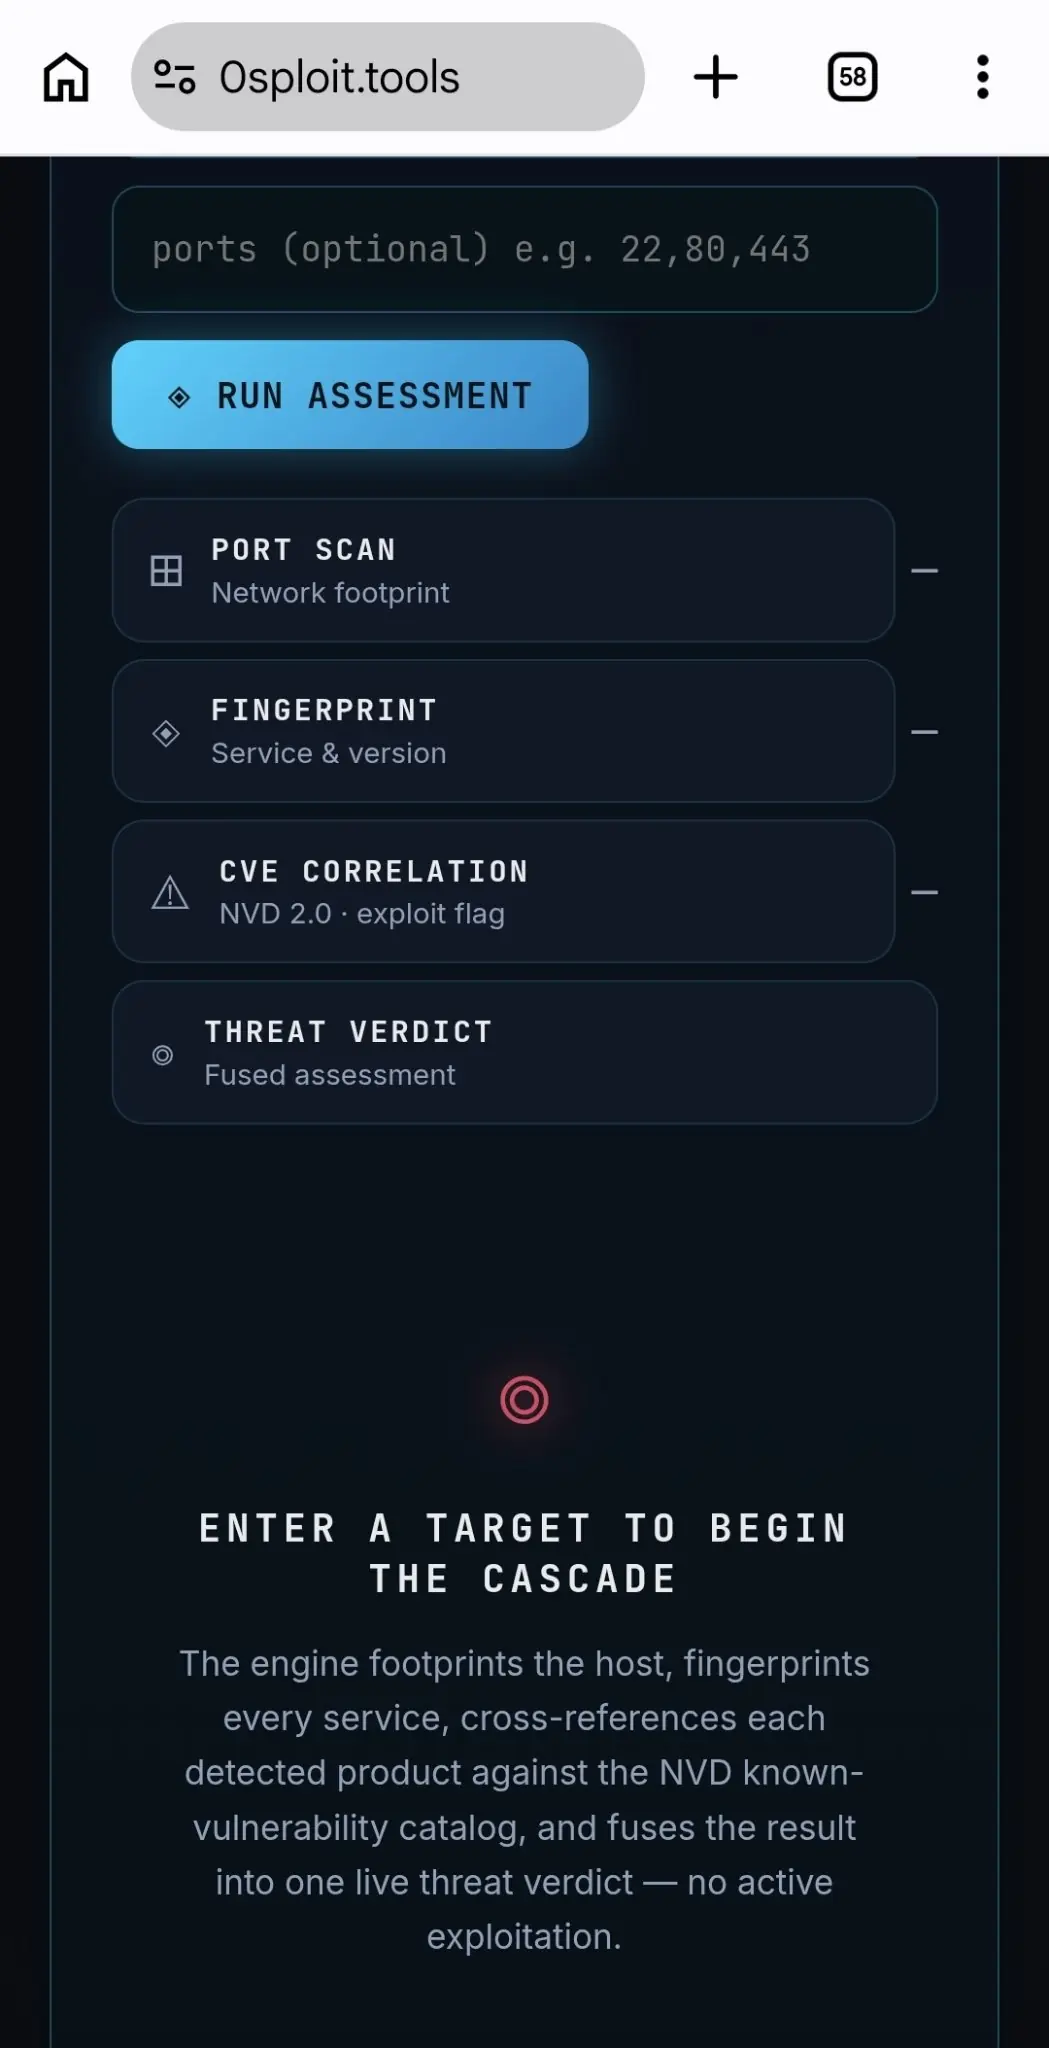
Raw scan output is not a decision. The Intel Engine progresses from visible exposure to a fused verdict, keeping each step inspectable.
Identify the exposed network surface on the authorized host.
Resolve listening services and the versions they report.
Cross-reference detected products against NVD records and exploit-availability flags.
Fuse findings into a concise assessment an operator can act on.
Inside the workbench
Move from evidence gathering to protocol and coverage-guided testing in one operator environment. Select a capability to inspect the real interface.
The audit pipeline scans an authorized target, fingerprints every service, correlates products and versions with NVD 2.0, then ranks the result with exploit-availability context.
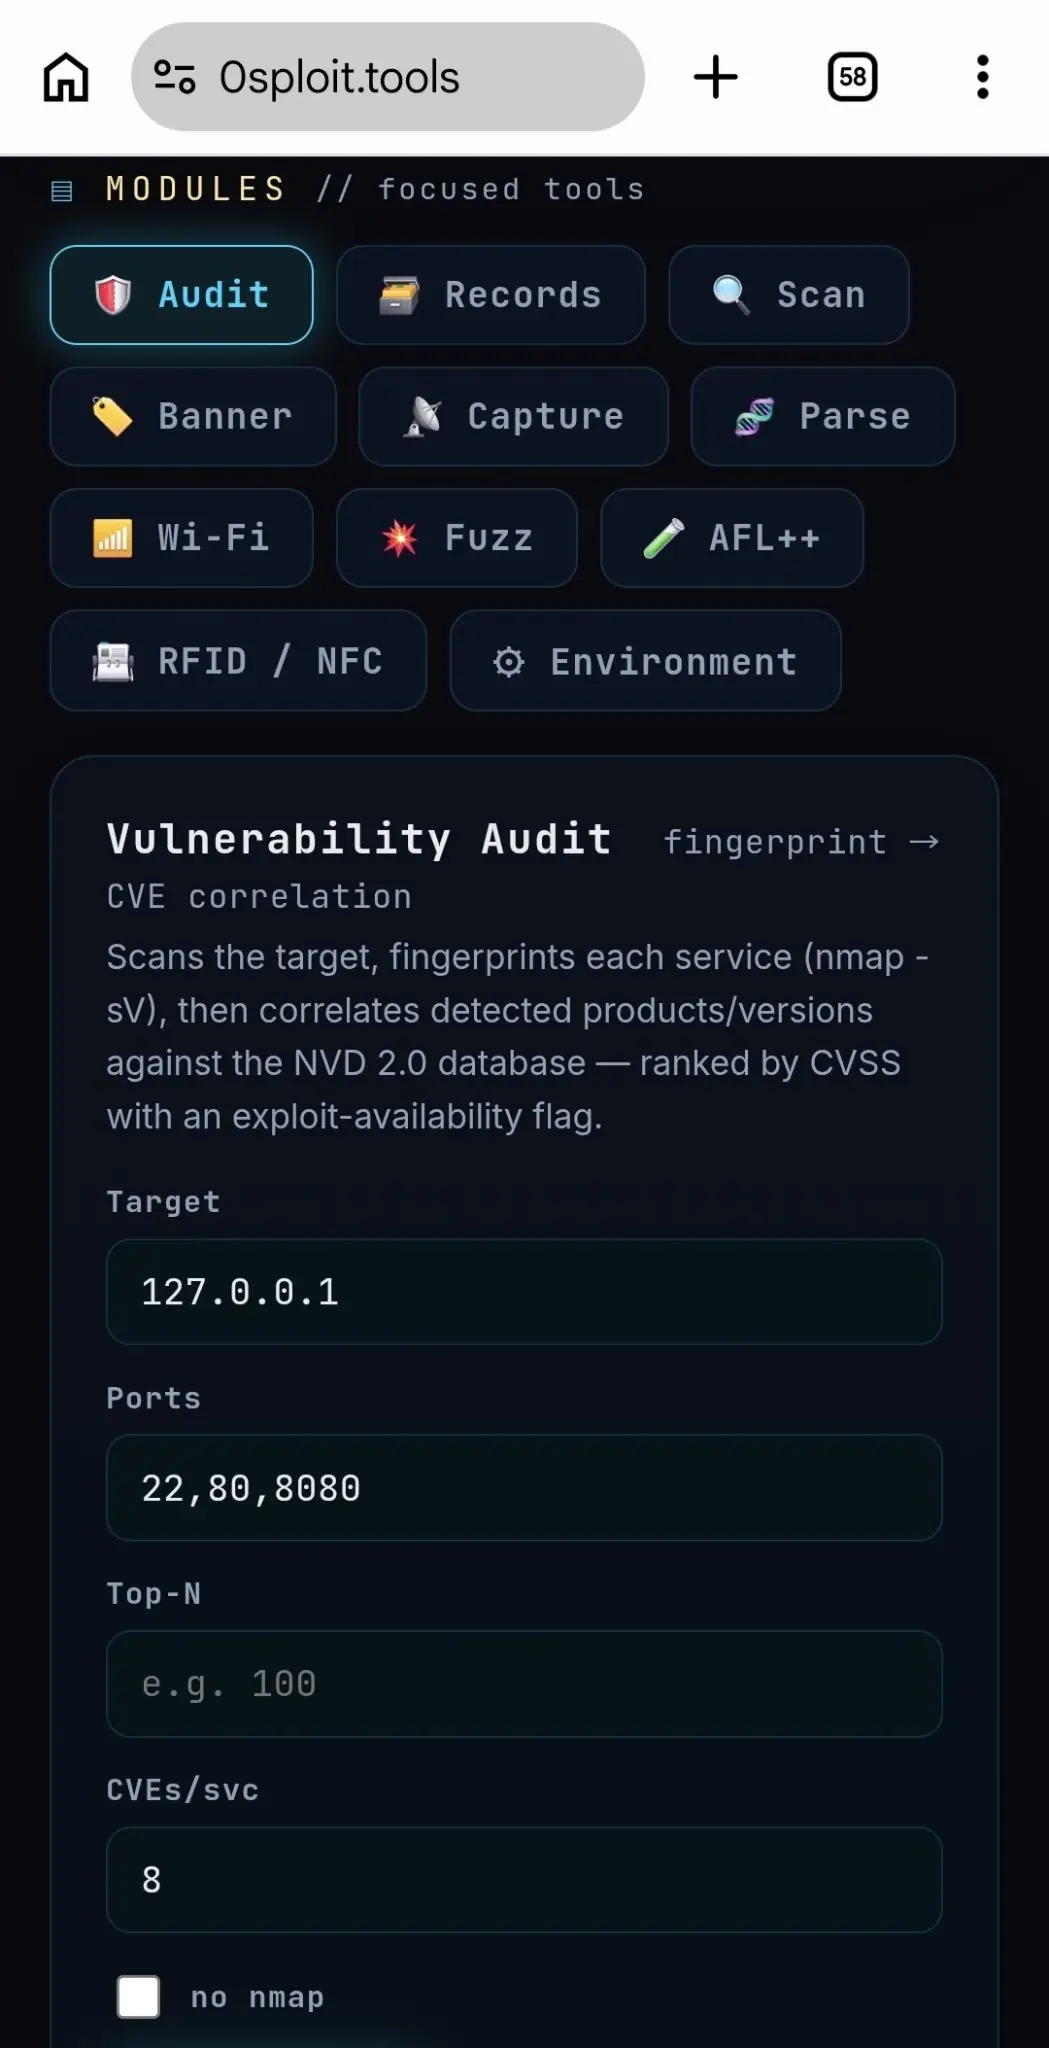
Interface imagery is from the deployed toolkit. Fuzzing sends malformed traffic and may destabilize a target; use only with explicit authorization.
Focused modules
01 // AUDITFingerprint services and correlate known risk.
02 // RECORDSKeep findings organized for review.
03 // SCANMap the visible surface of an approved target.
04 // BANNERInspect exposed service responses.
05 // CAPTURECollect evidence from controlled traffic.
06 // PARSETurn raw inputs into useful structure.
07 // WI-FIAssess wireless context in approved environments.
08 // FUZZExercise service handling with controlled mutations.
09 // AFL++Run instrumented coverage-guided campaigns.
10 // RFID/NFCWork with close-range radio artifacts.
11 // ENVInspect the available security toolchain.
12 // INTELFuse assessment stages into one readable verdict.
13 // WARDRIVEWiGLE & Kismet survey ingestion and AP telemetry.
14 // GOD'S EYE3D geospatial cyber target overlay and radar stems.
15 // KERNELKernel CVE advisory correlation and sysctl posture.
The operating boundary
Assess only systems you own or have explicit written permission to test.
The assessment workflow identifies known exploit availability; it does not execute an exploit against the target.
Mutation engines transmit malformed traffic and can crash or destabilize a service. Run them only in an isolated lab or expressly authorized scope.
The toolkit exposes each step and its risk so trained users can make deliberate decisions.
Ready when your scope is
Open the red-team workbench for authorized integrity testing, or explore the wider Zero-Day Dynamics intelligence platform.